

Every risky step in its own sealed machine.
When an AI agent runs code, a file is opened or a build runs, it happens in a throwaway machine with only the memory and network access it needs. When the step ends, the machine is gone. Every refusal is recorded, without anyone seeing the code.
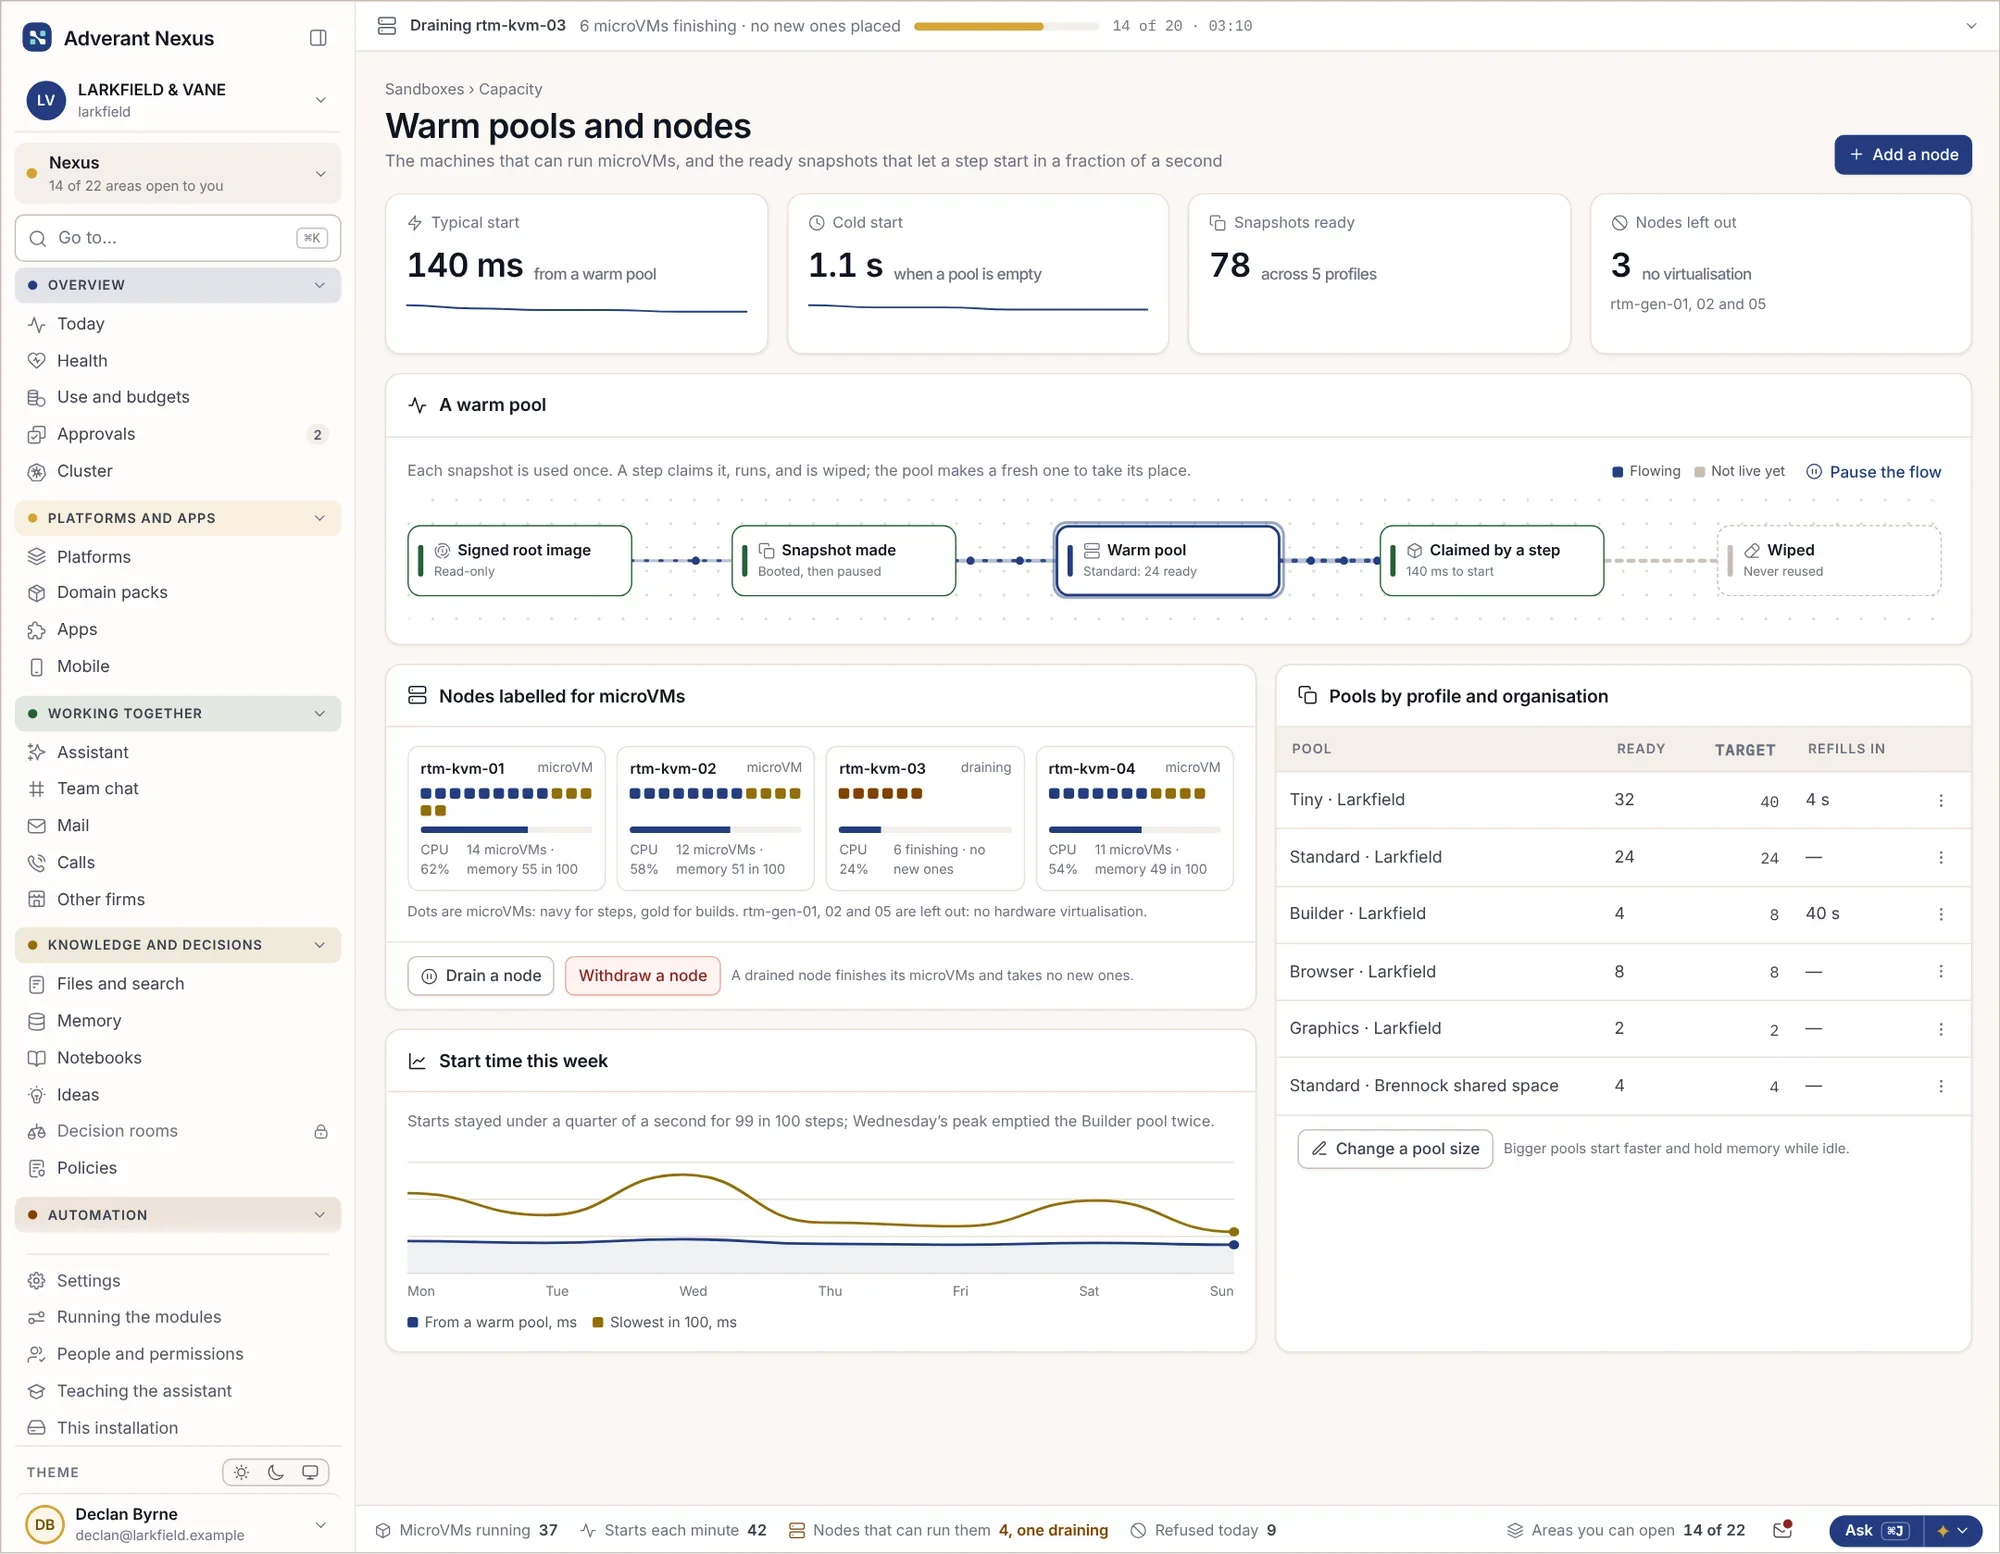
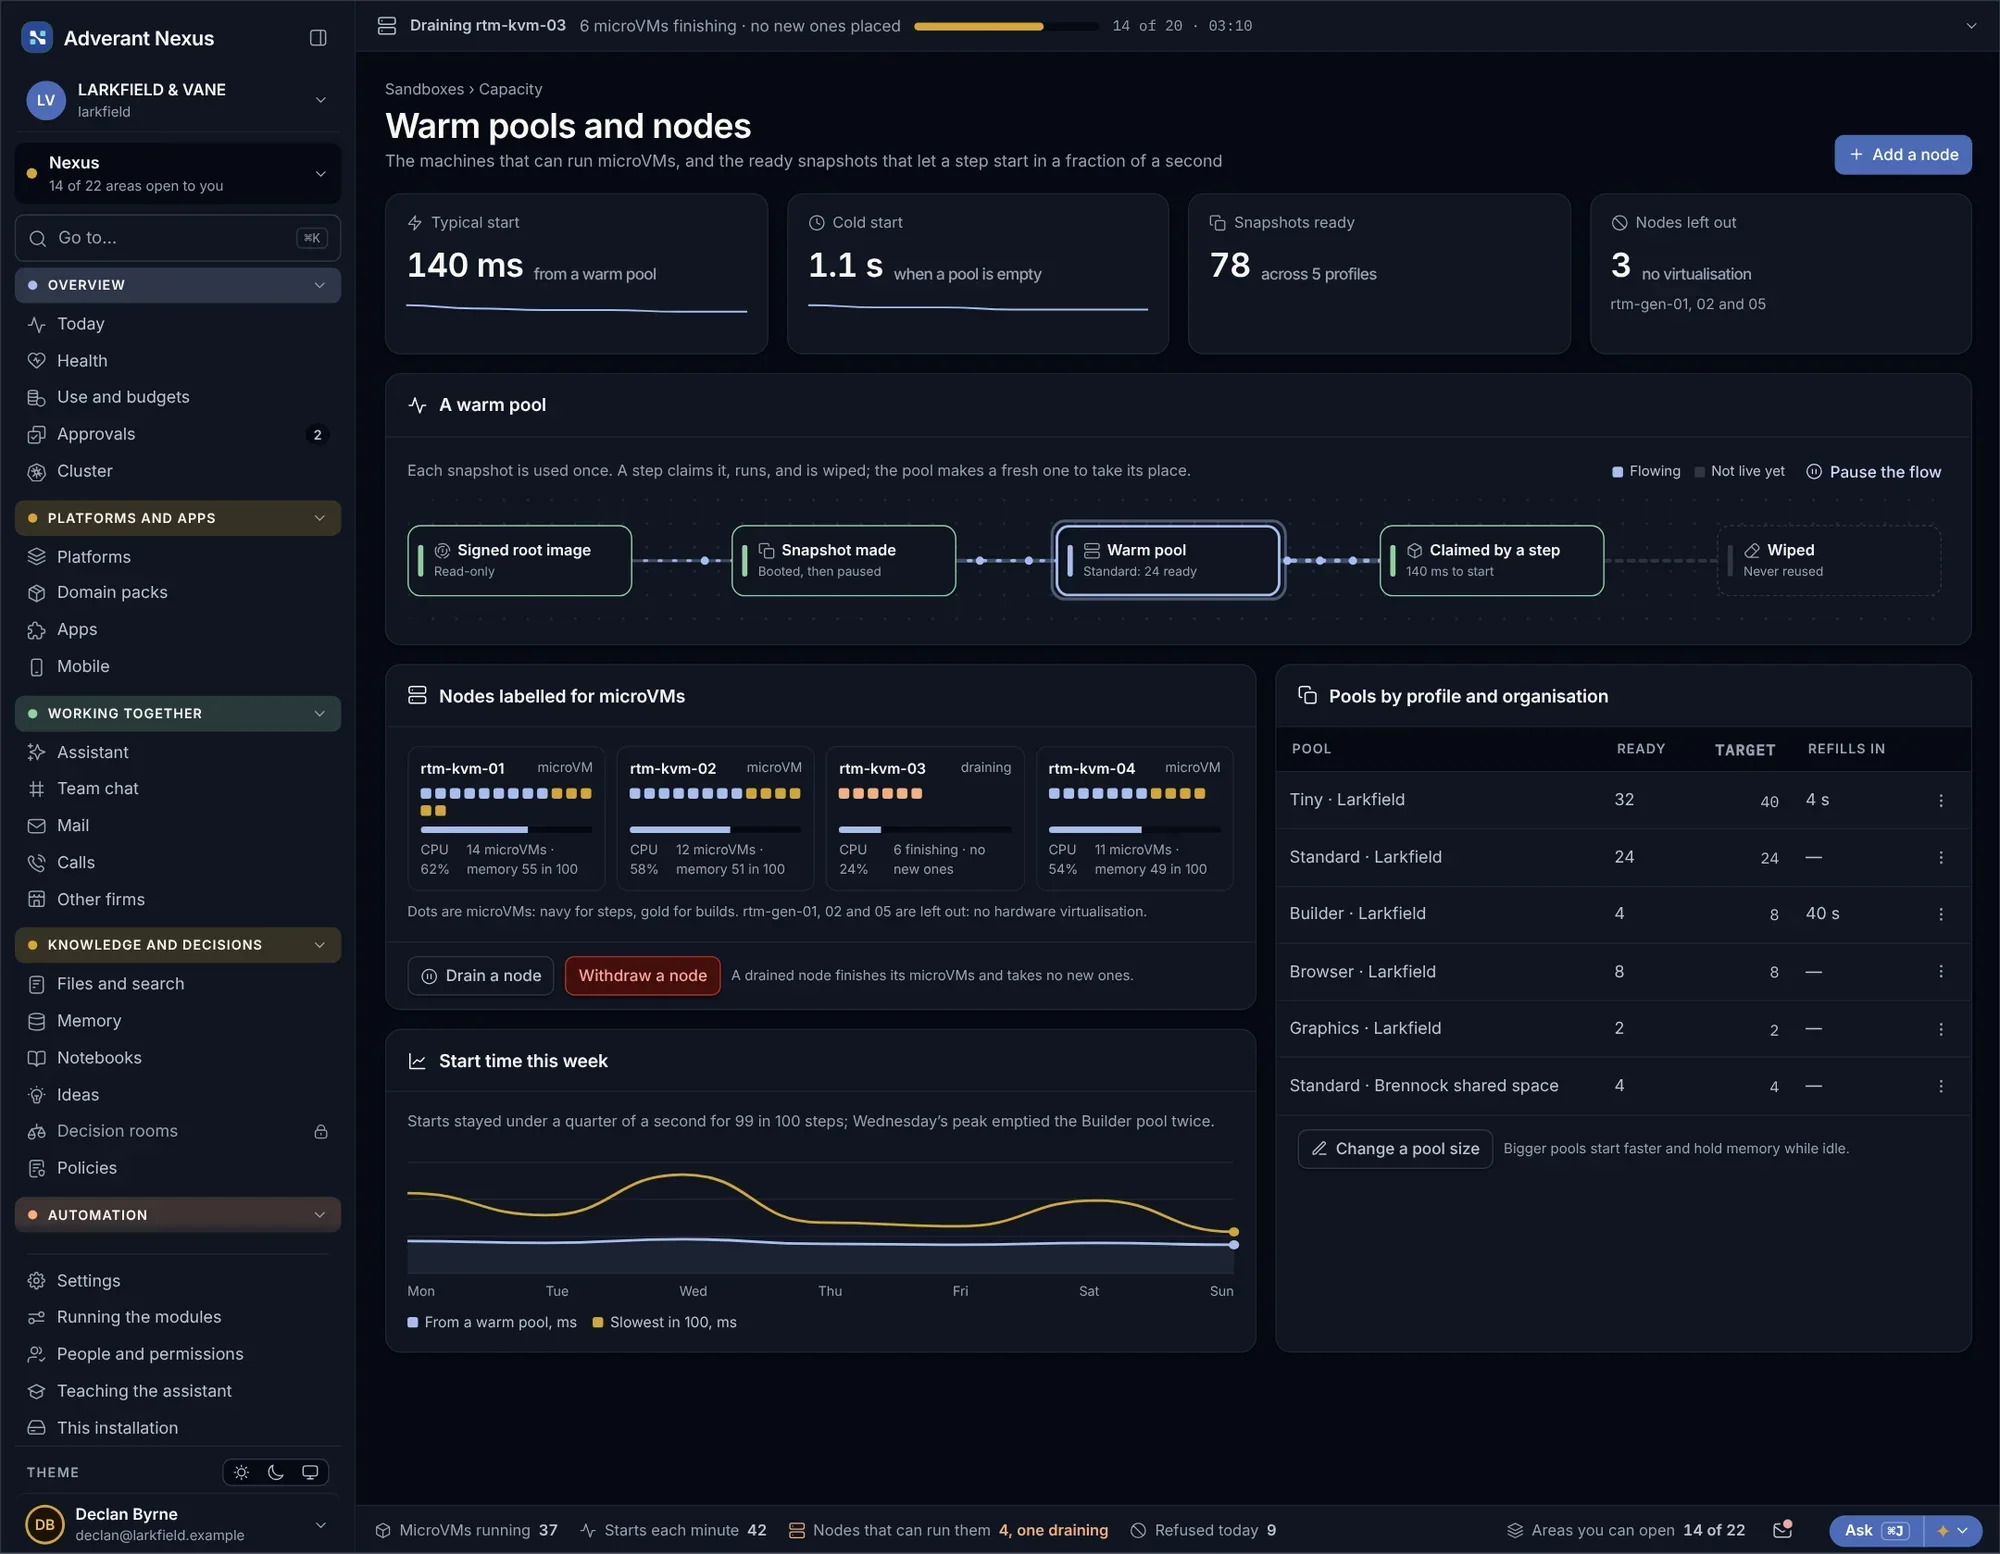
The right size, nothing more.
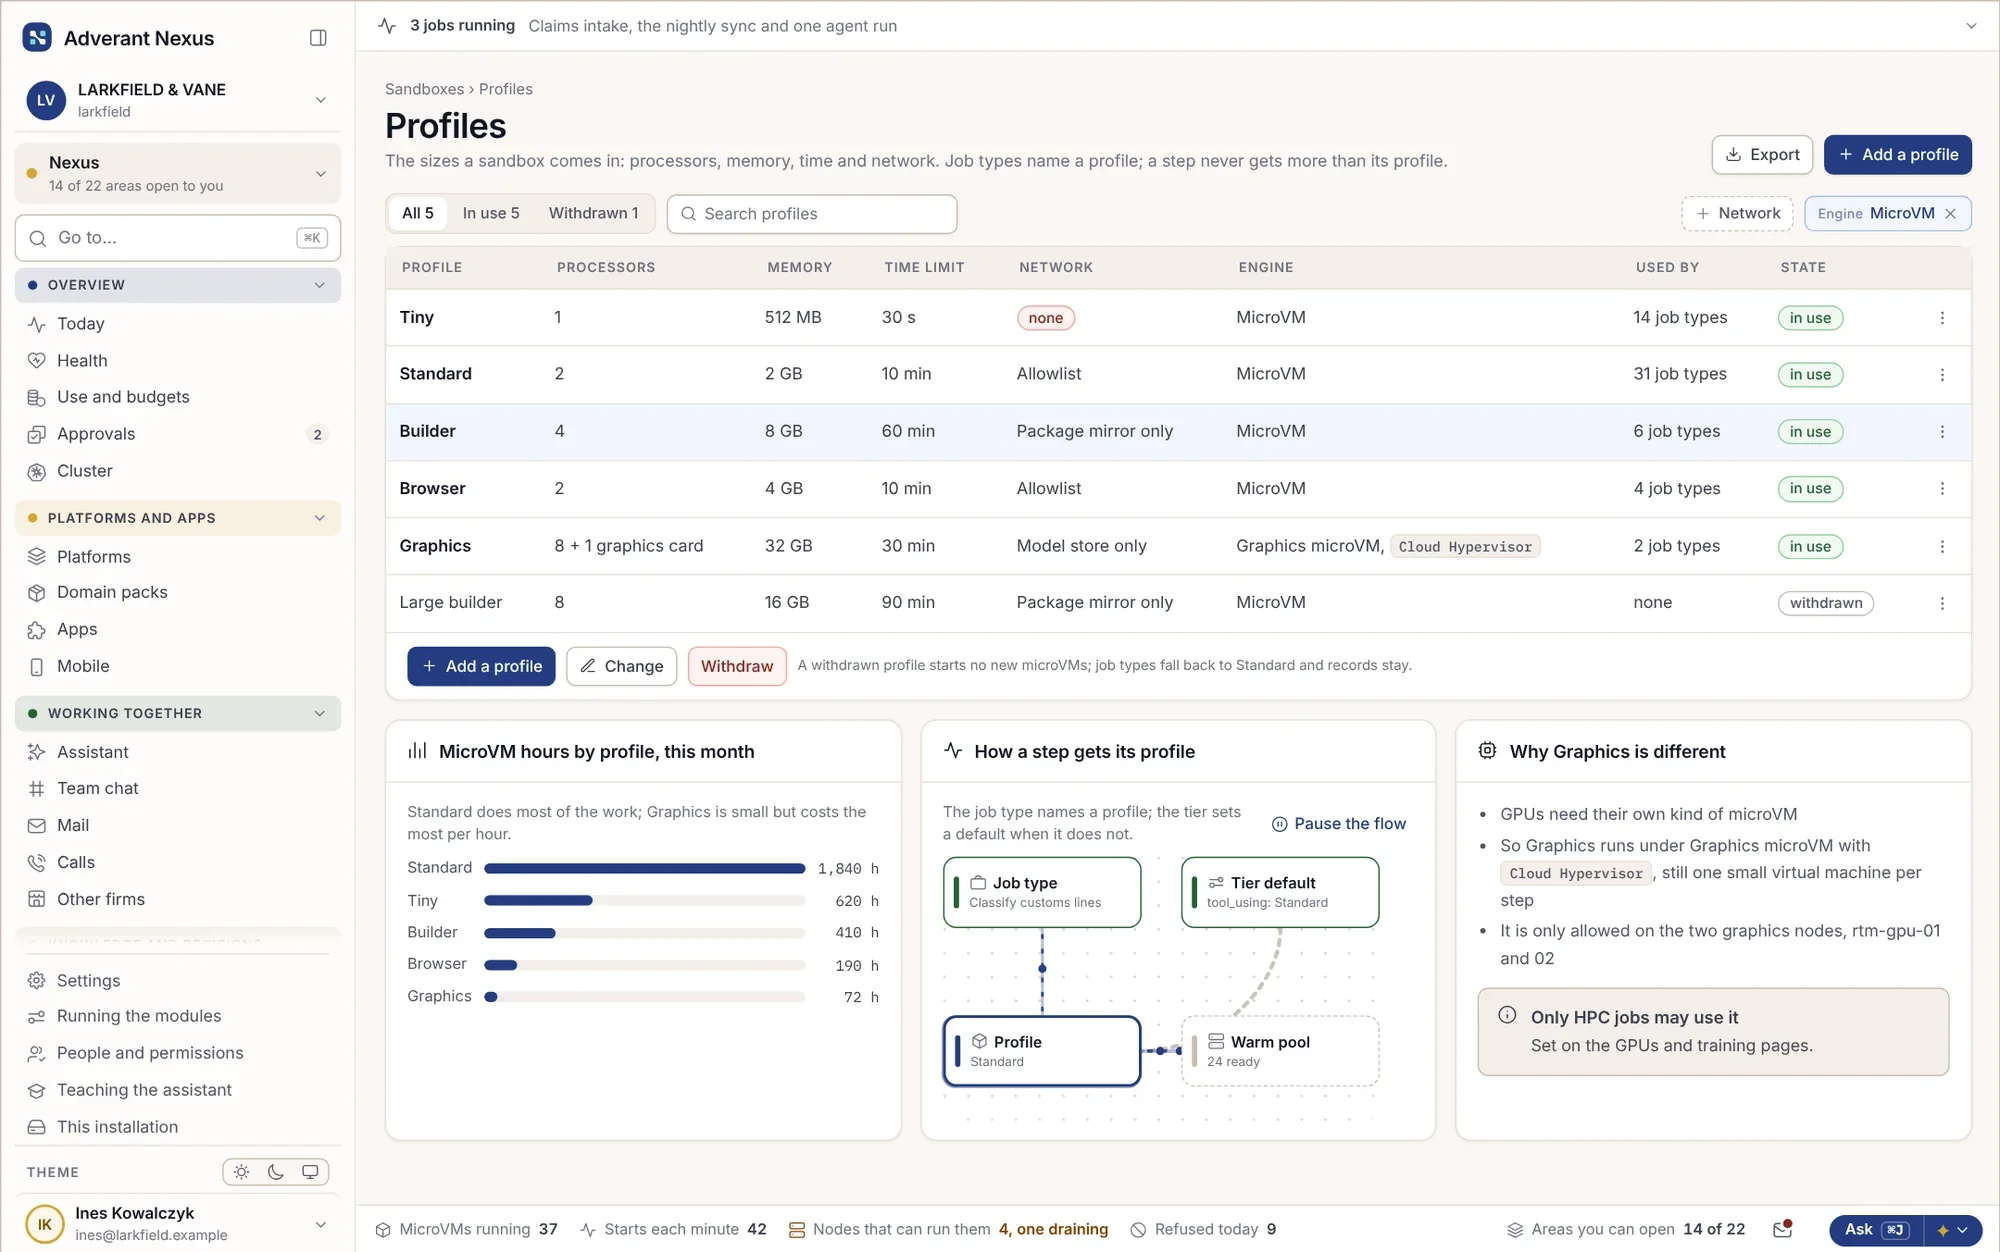
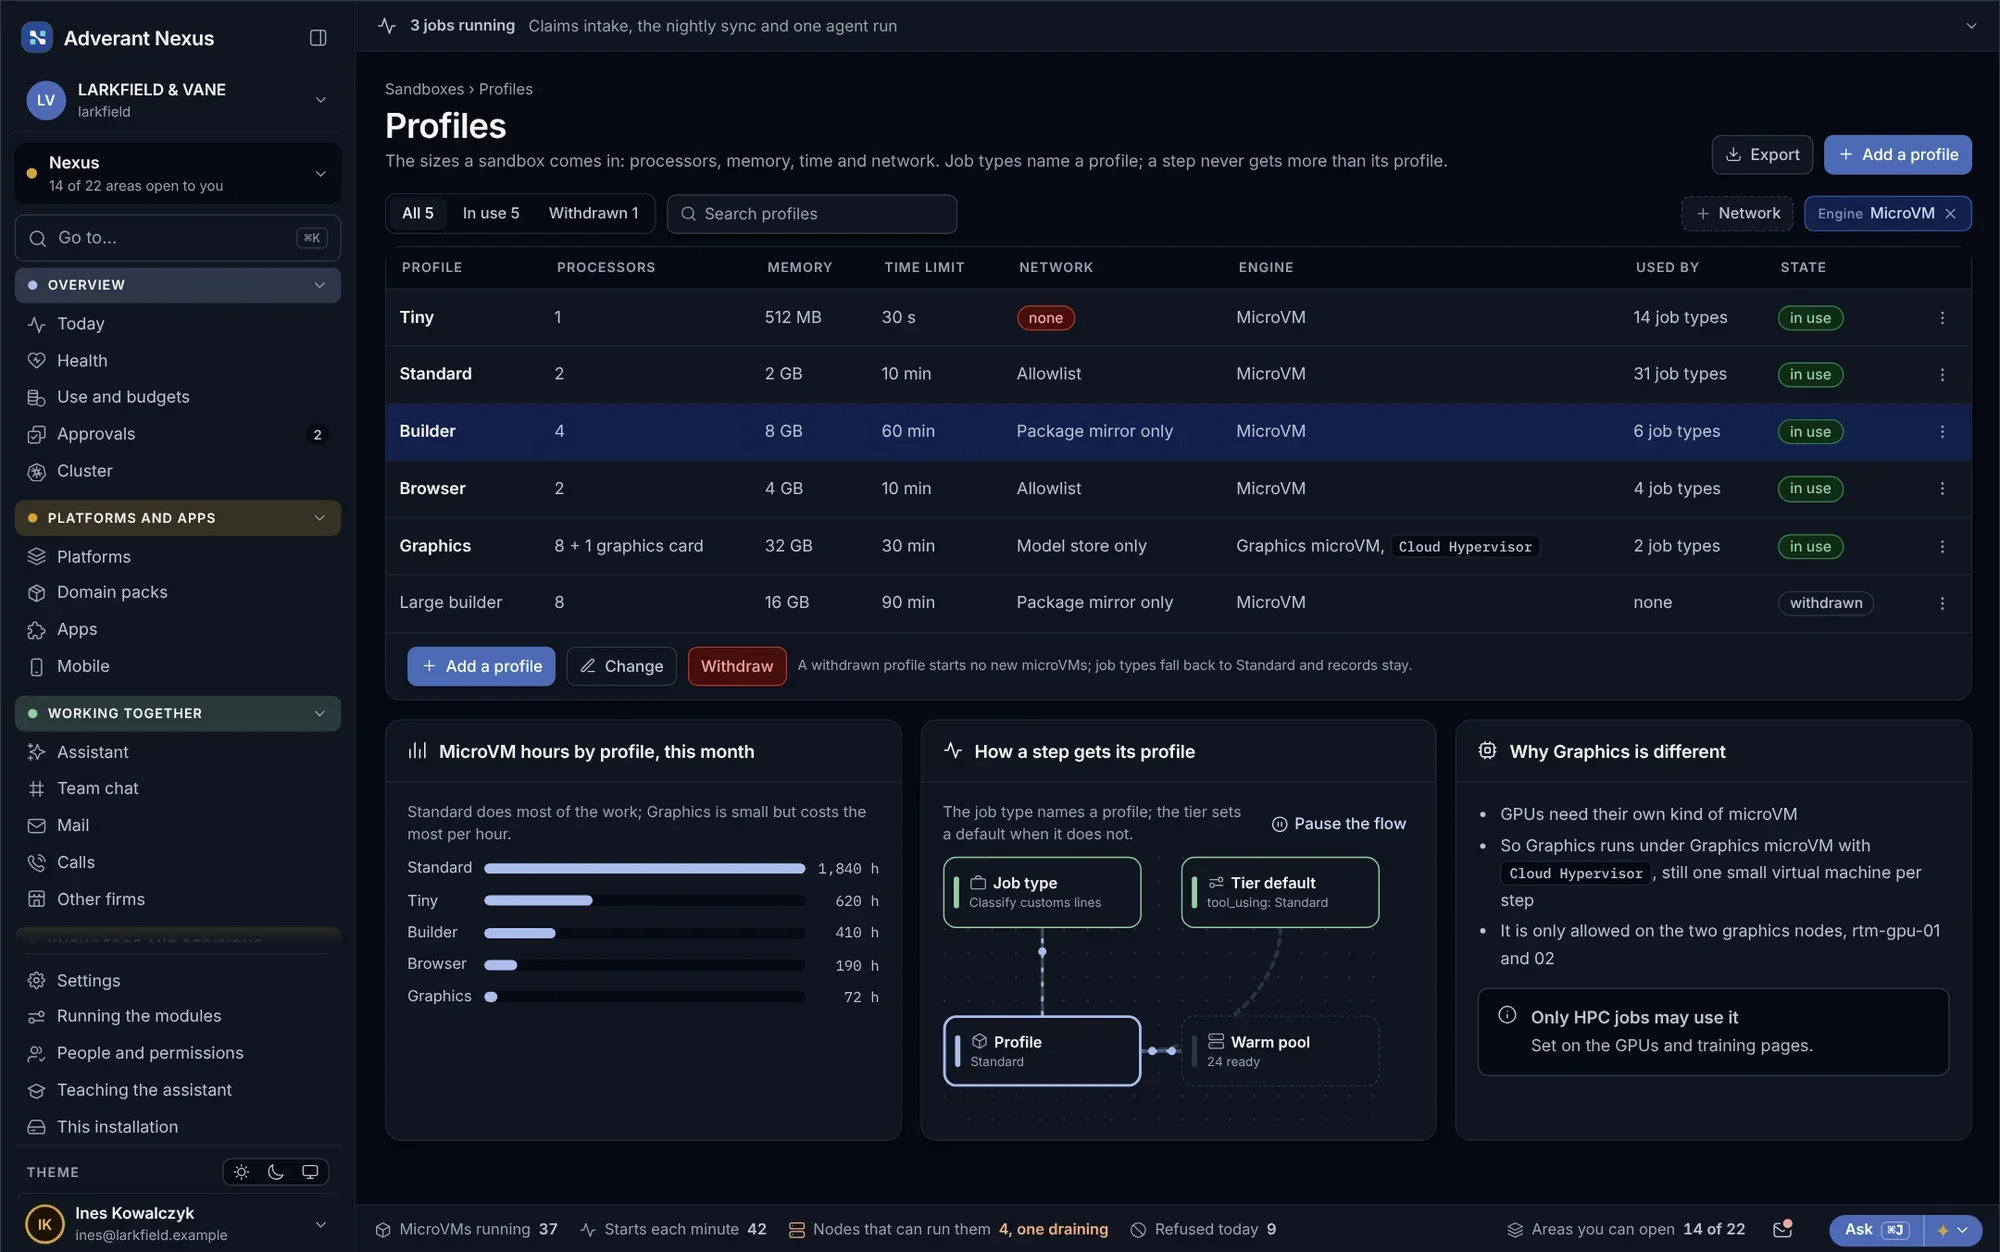
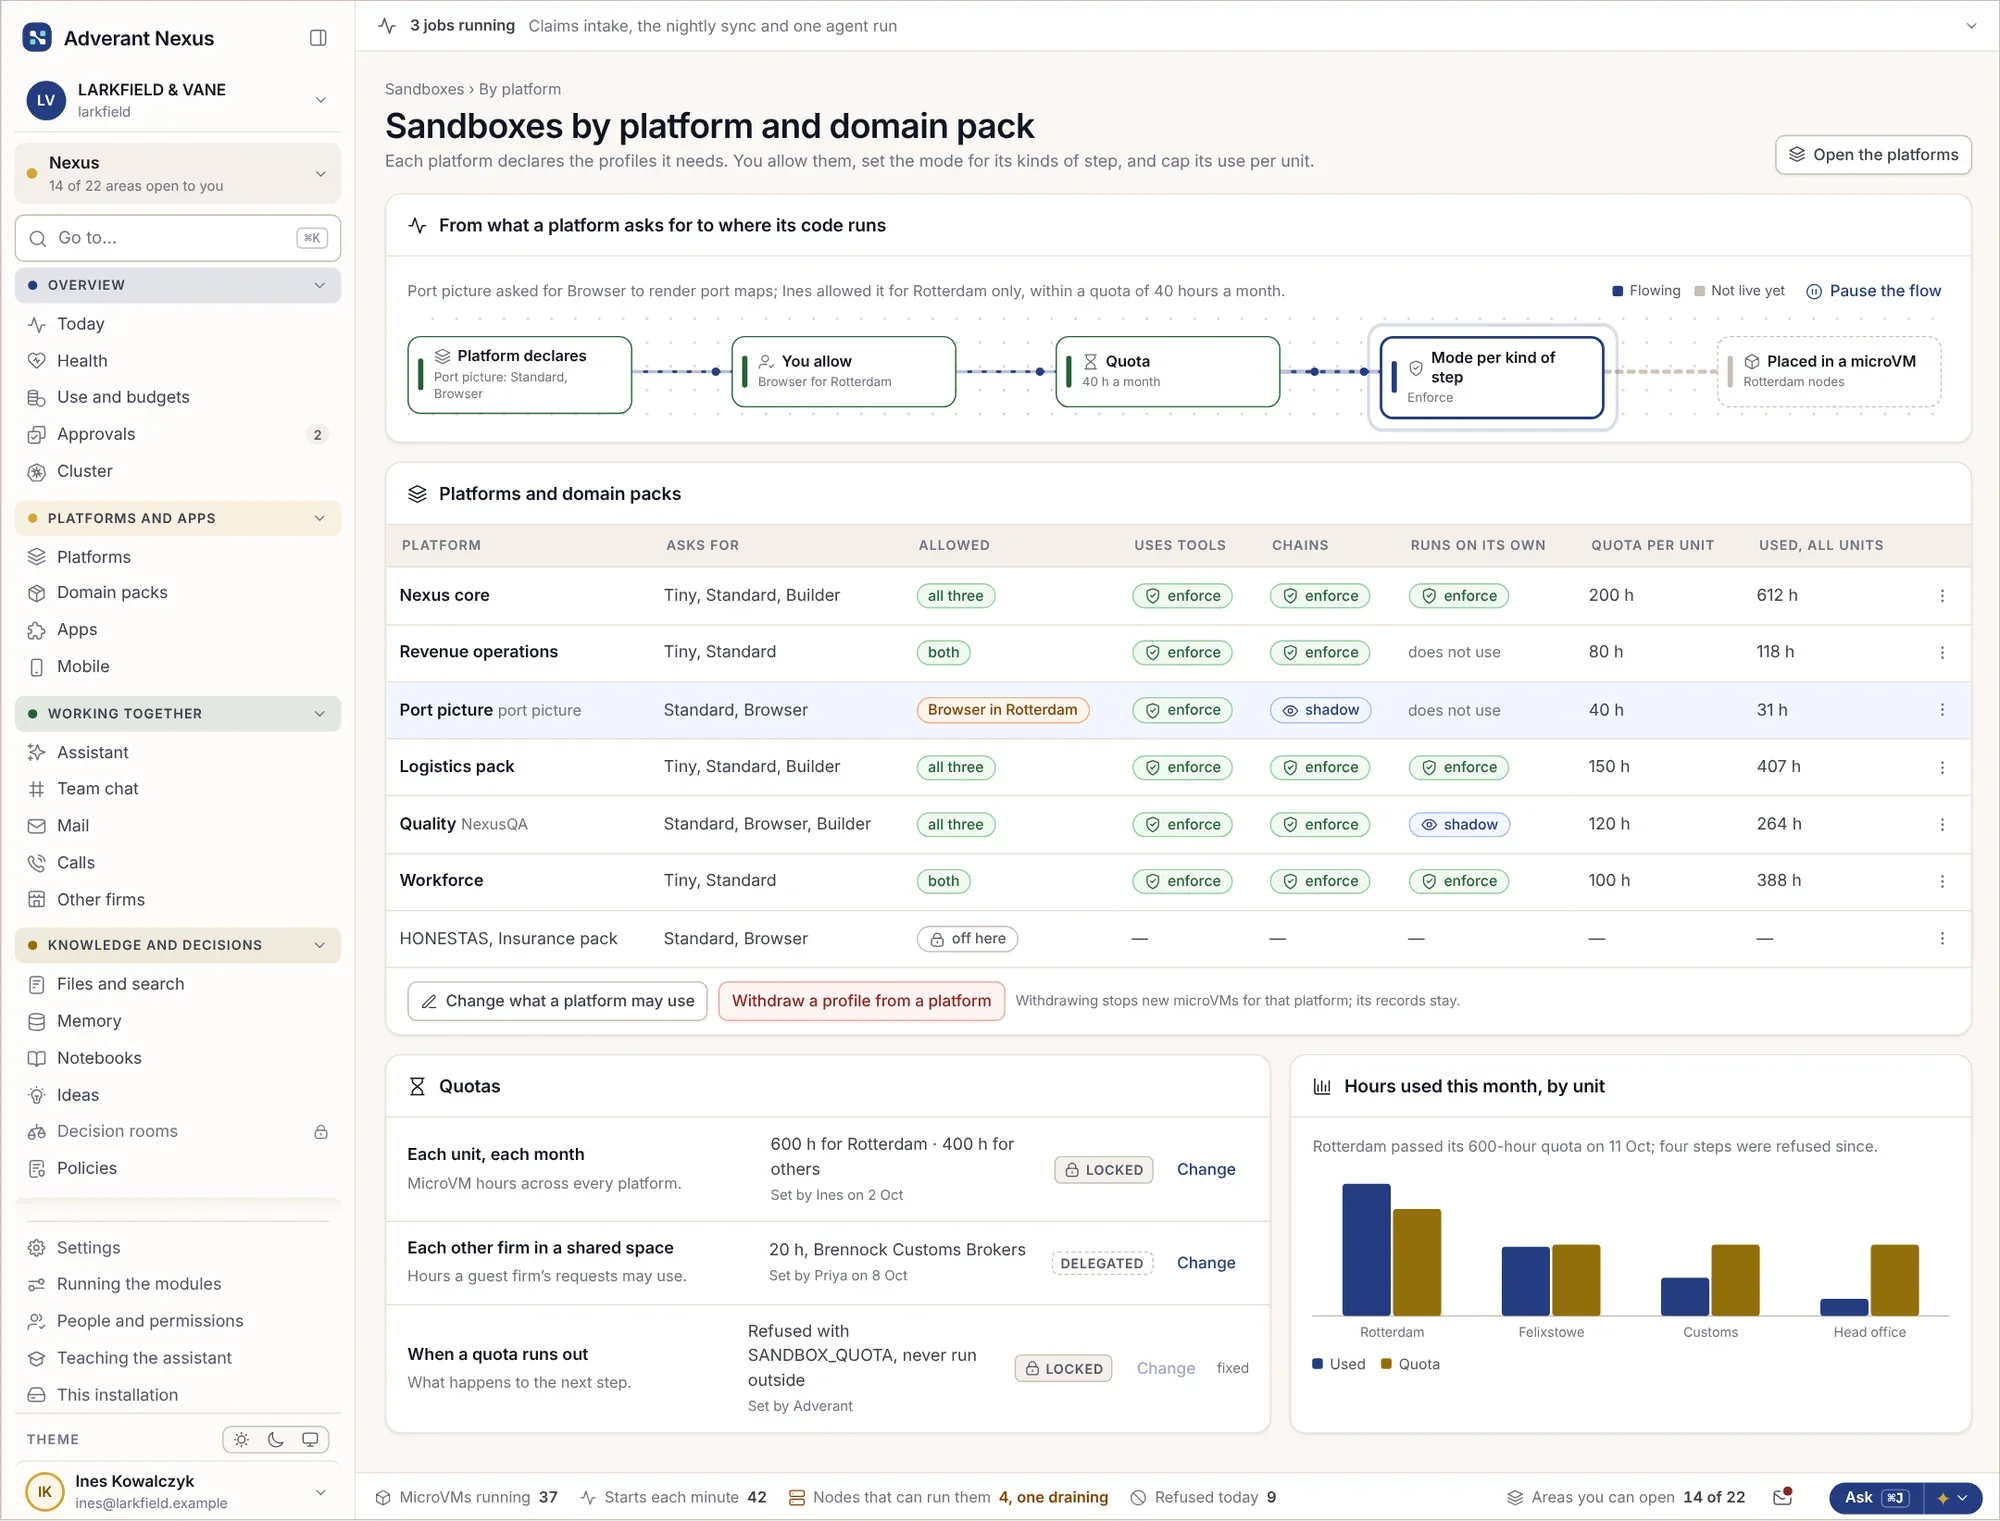
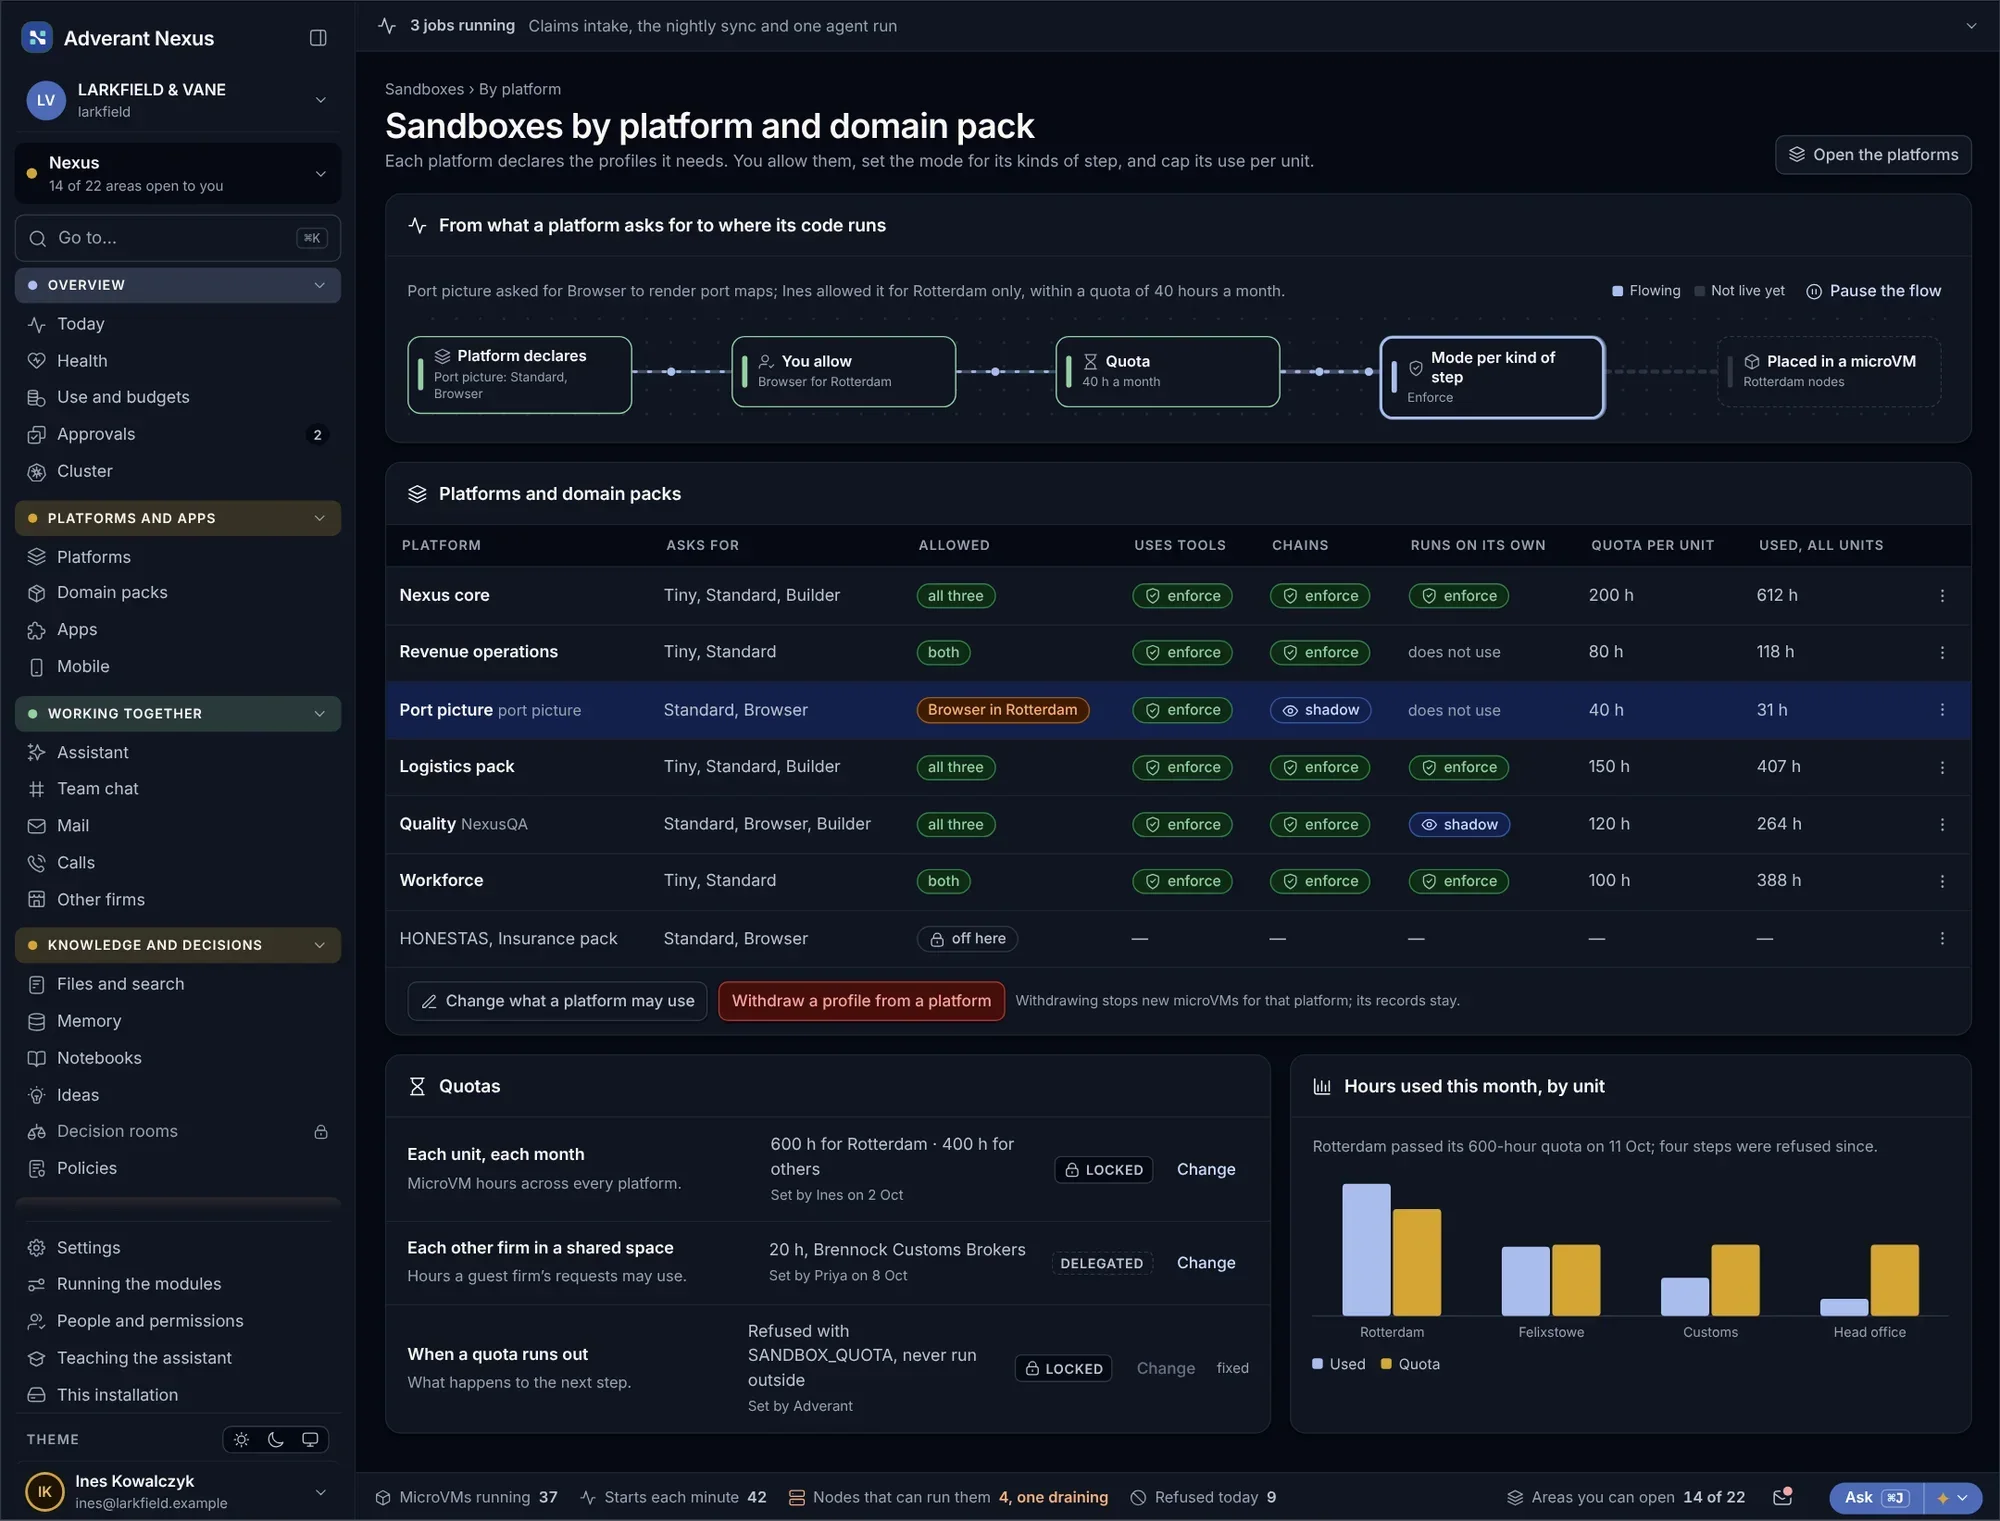
Profiles set the memory, time and network each kind of step may use. Each platform and domain pack is allowed only the profiles it needs.
Profiles
See the sizes and networks steps may run with, and who uses each.
- Memory, time and network
- Who uses each
- Changed with approval
Per platform and domain
- Allowed per platform
- Allowed per domain pack
- Refusals explained
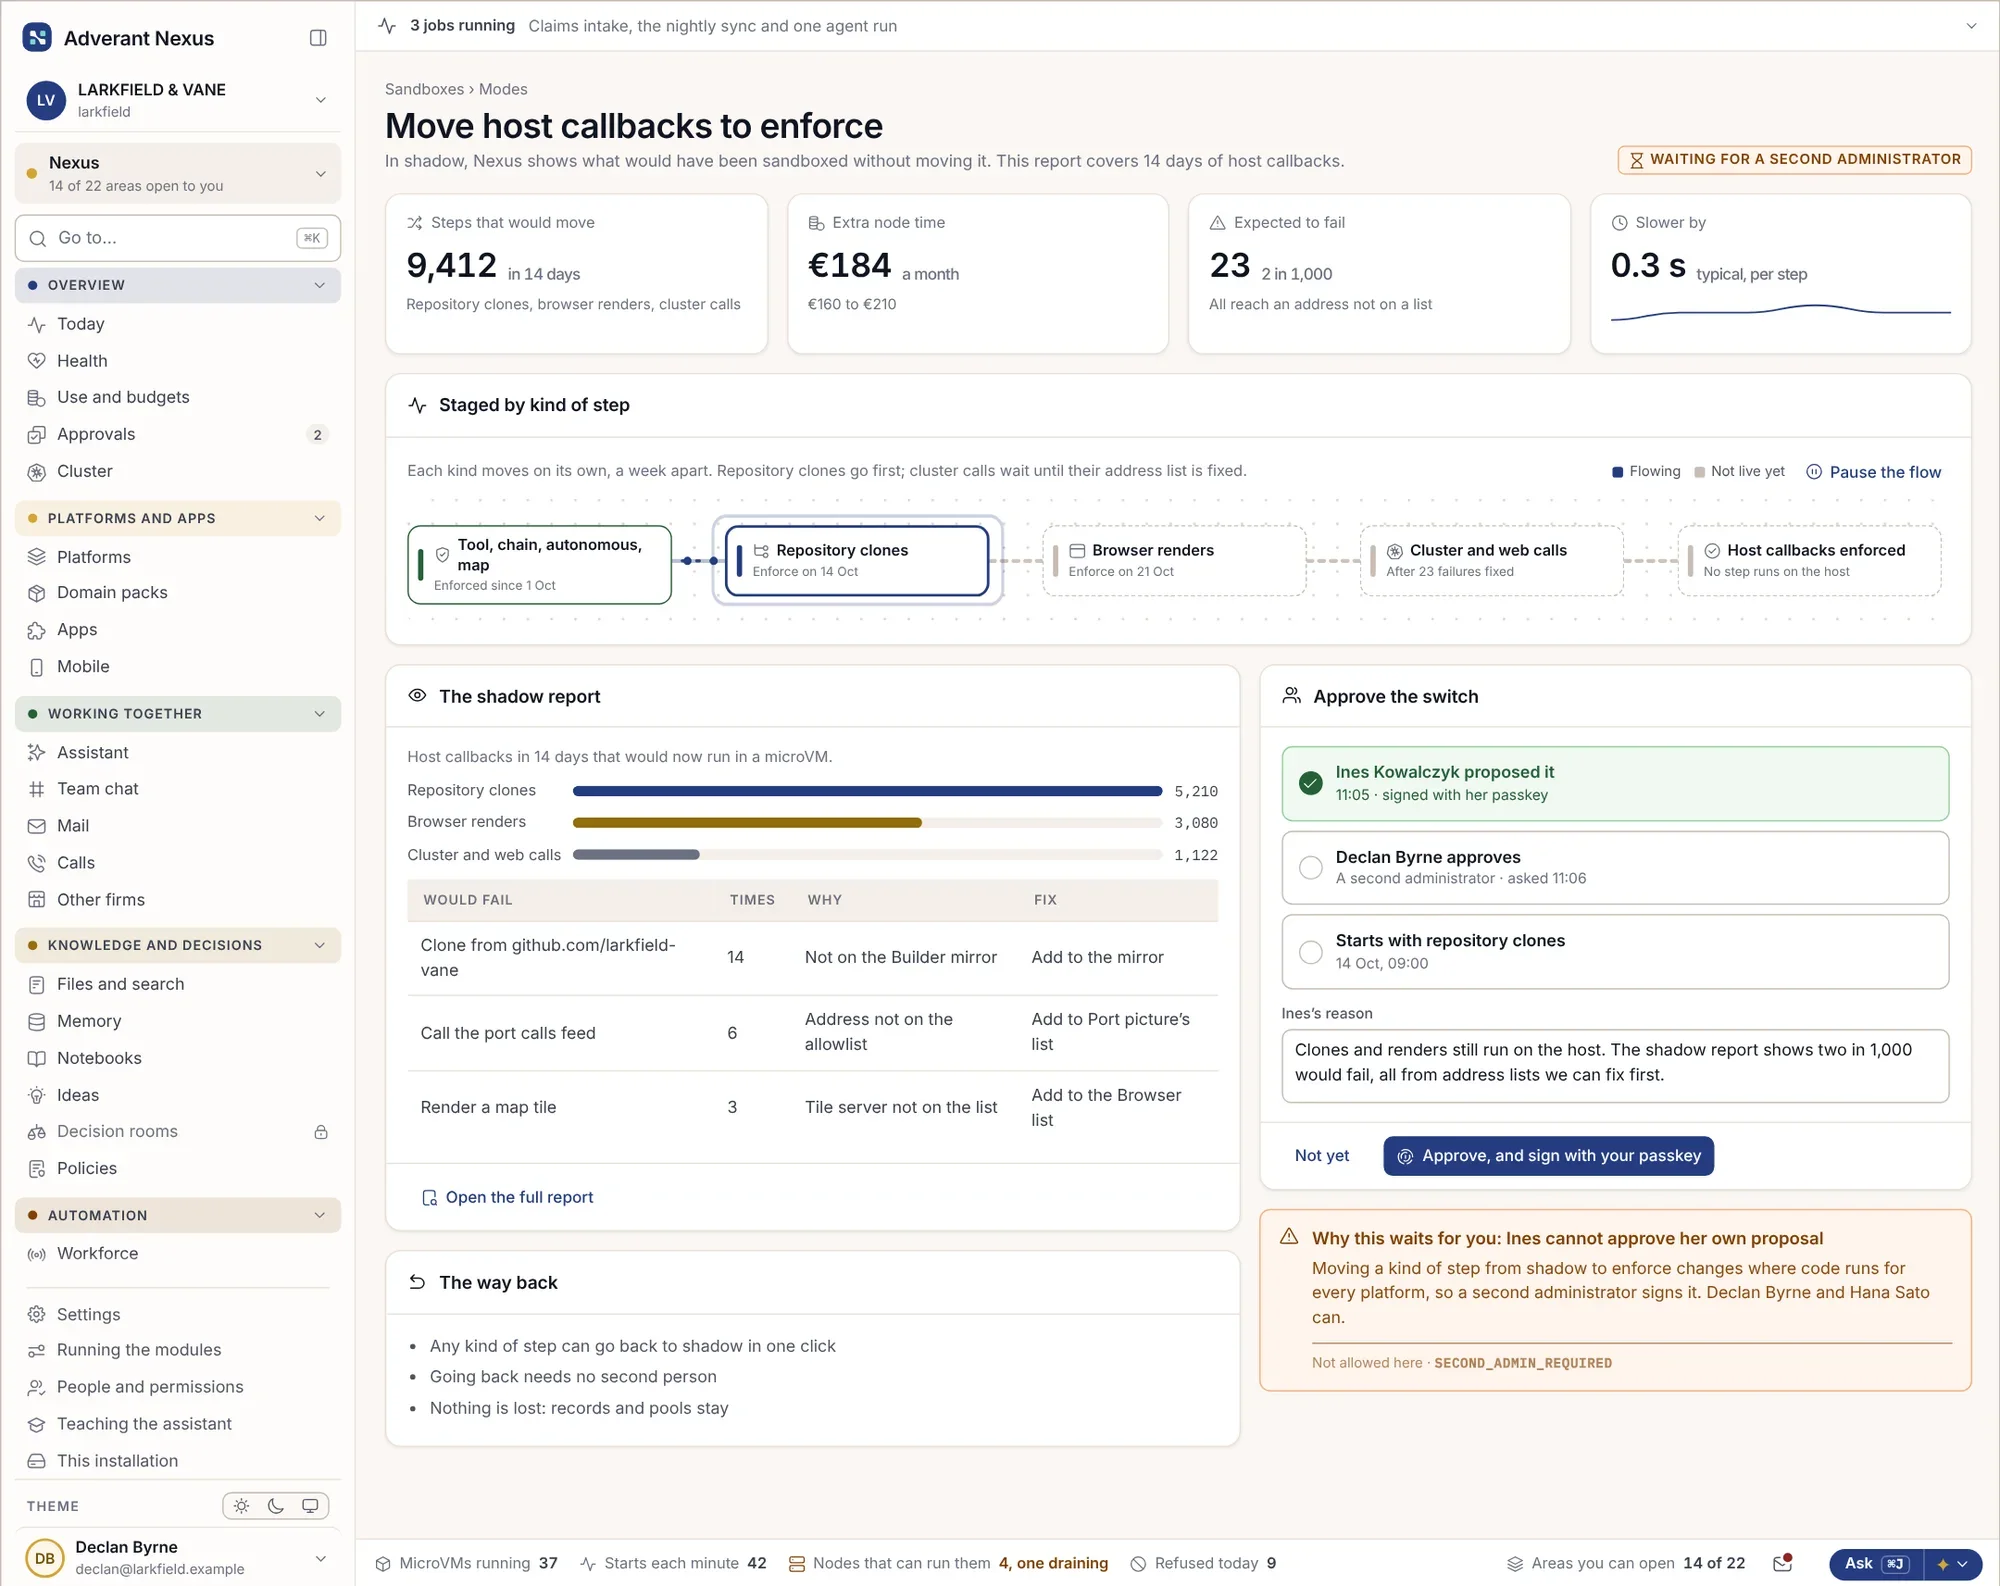
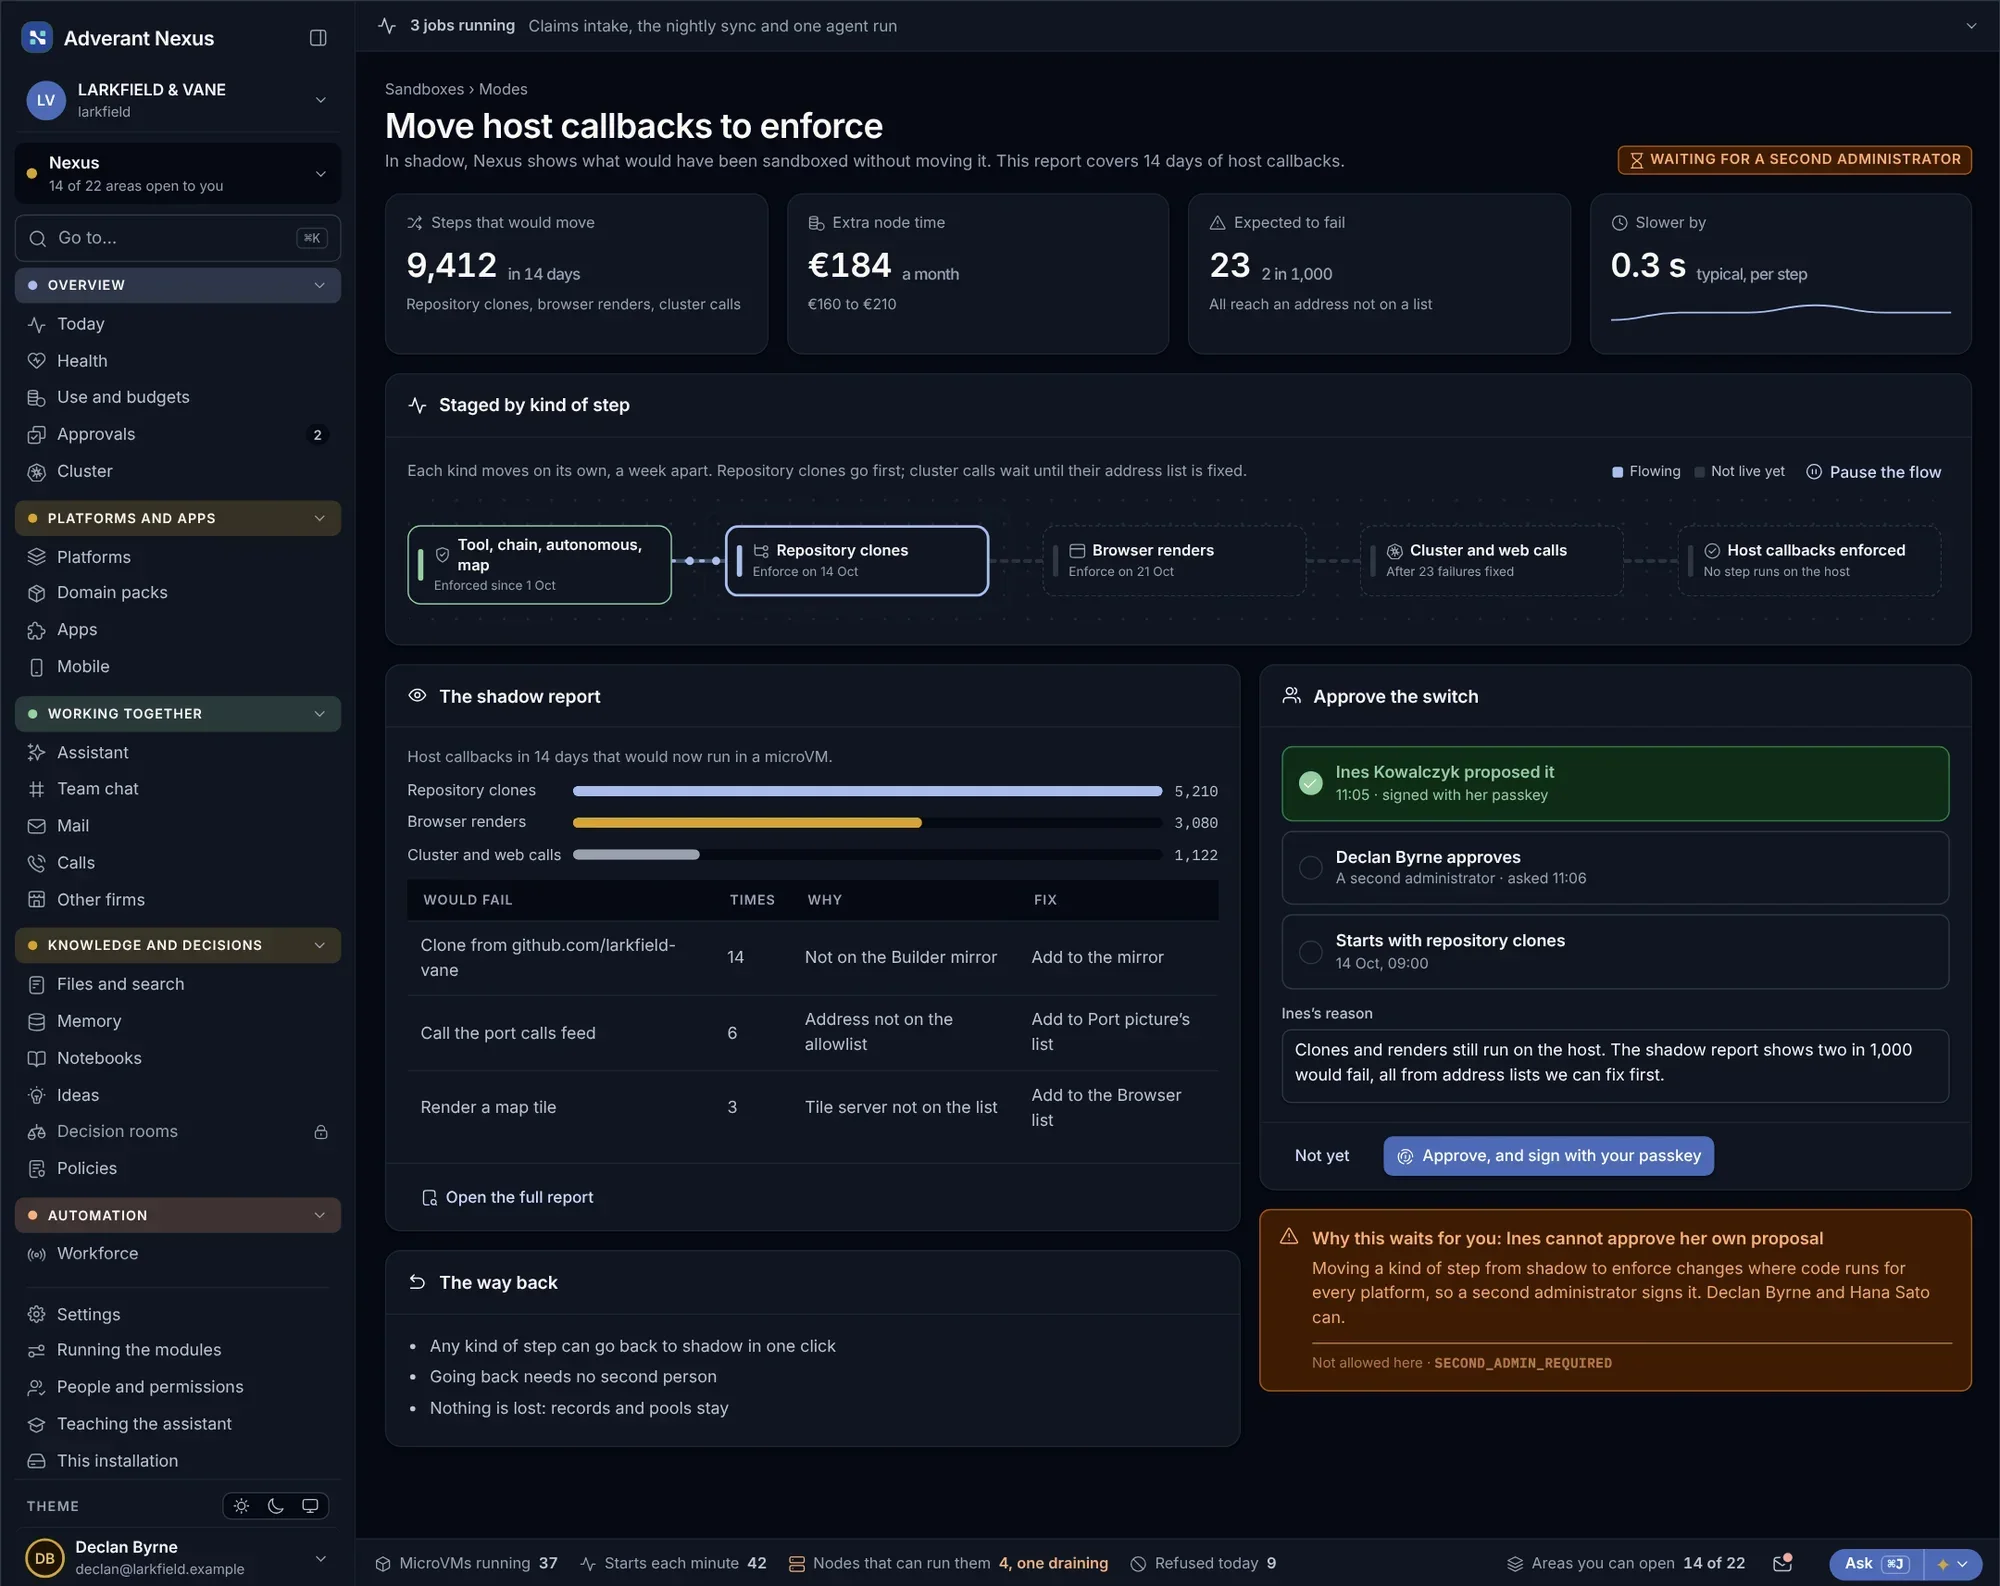
Tried in shadow, then enforced.
New limits run in shadow first, showing what they would have stopped. Then they are enforced, one kind of step at a time.
- Shadow mode first
- Enforced step by step
- Every change recorded
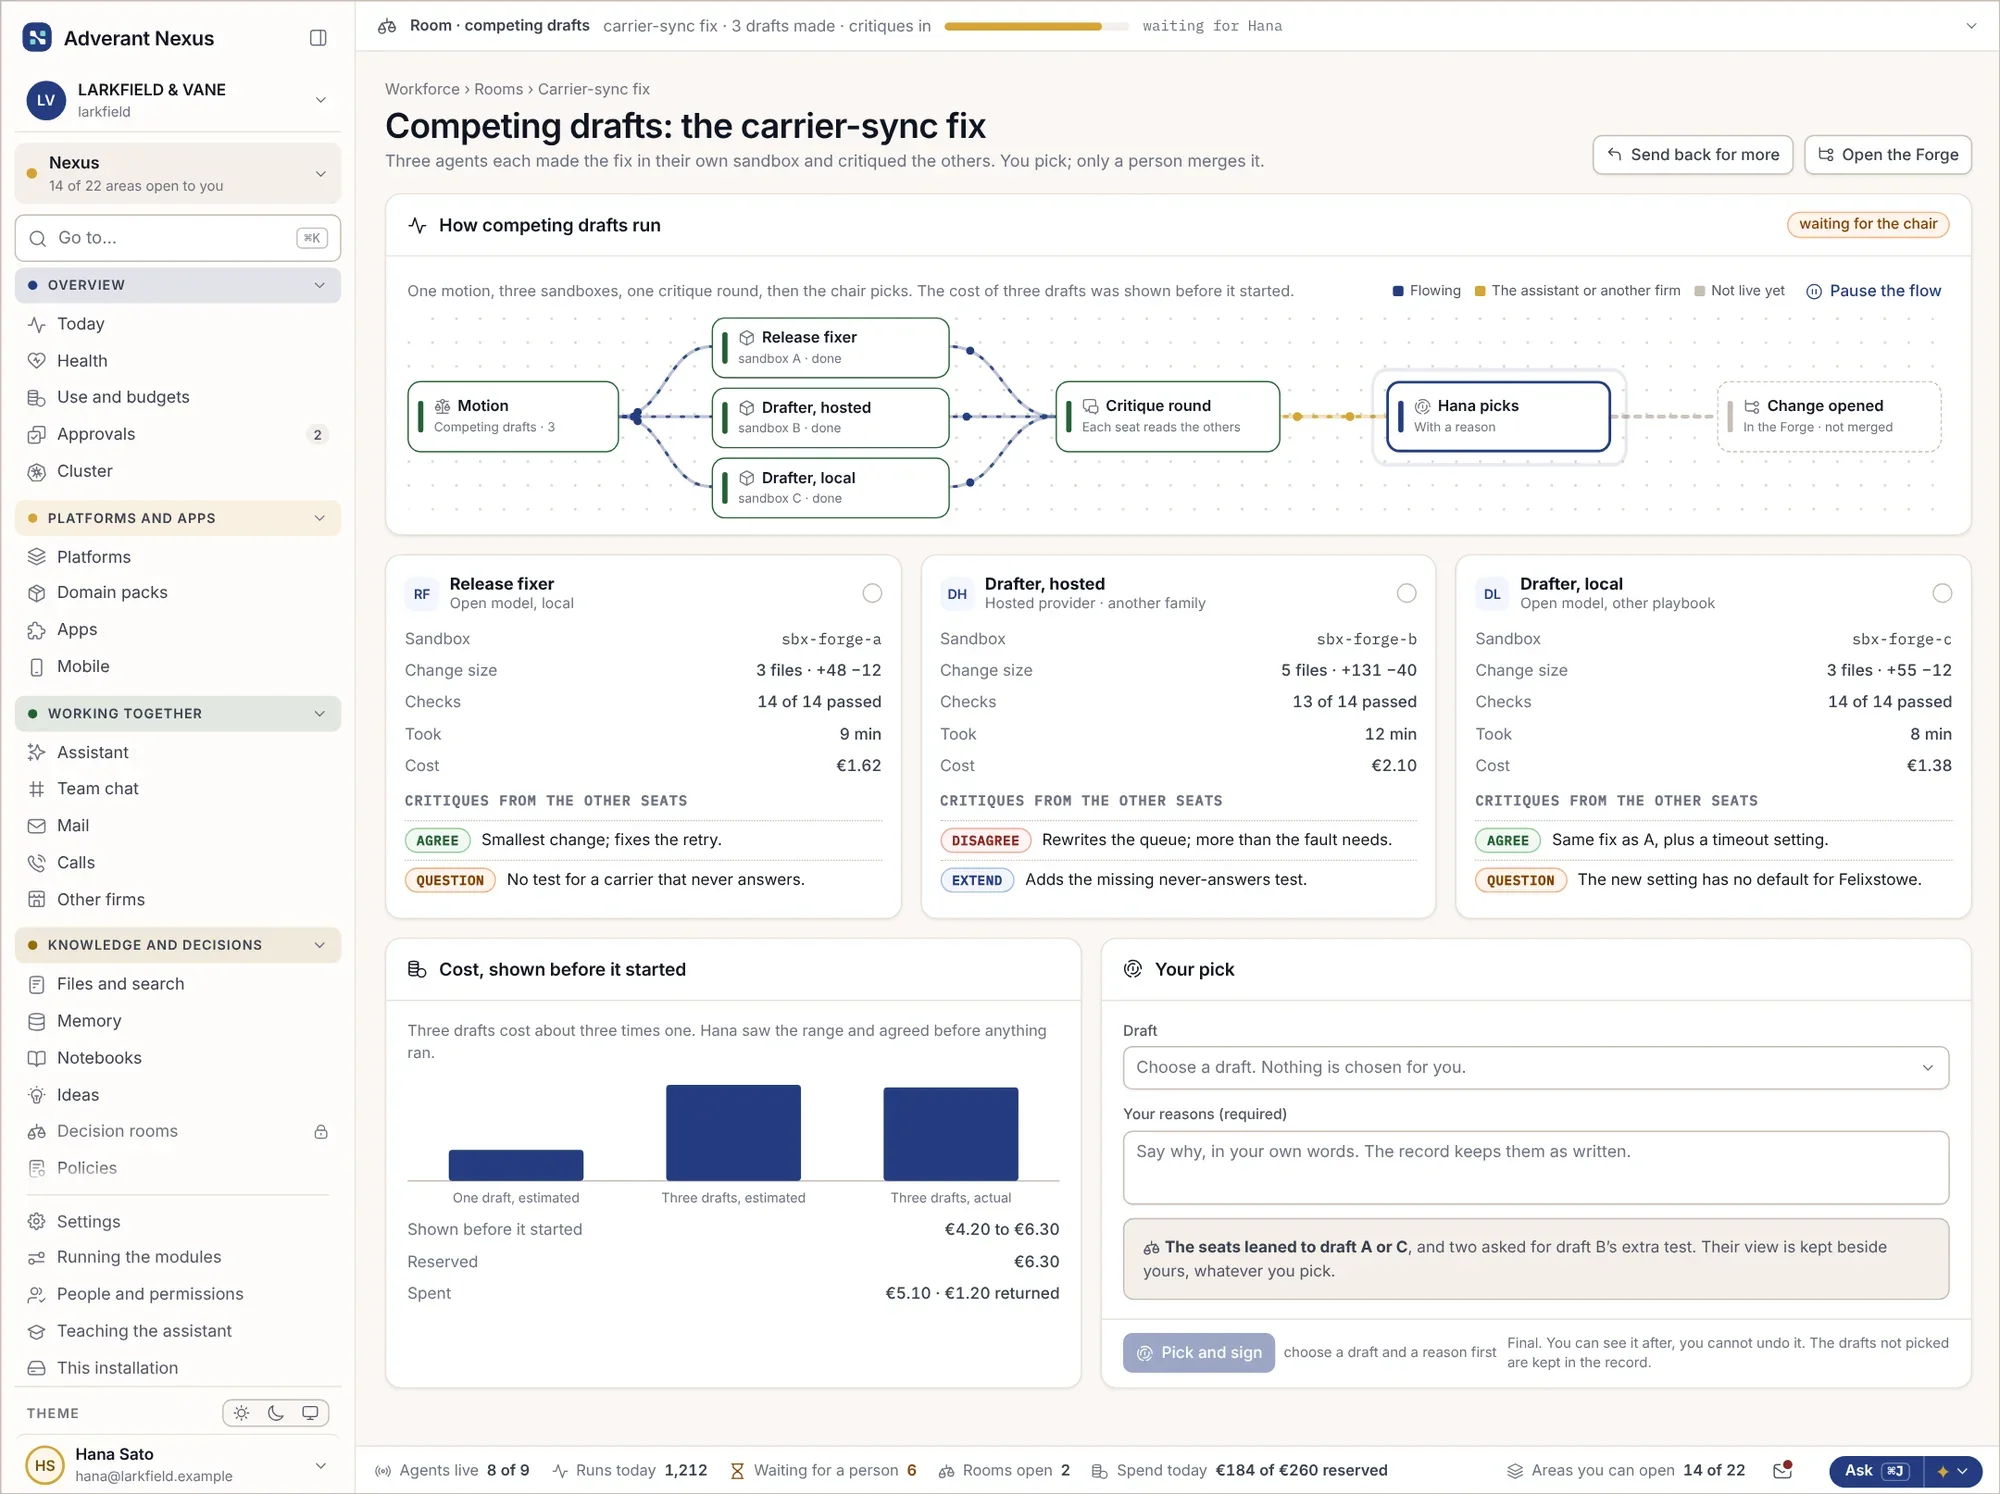
Three drafts, three sealed machines.
When an AI agent fixes something, it can make several drafts, each in its own sandbox, and a person picks the one to keep.
- Each draft isolated
- Compared side by side
- A person chooses
Who used what, without seeing the code.
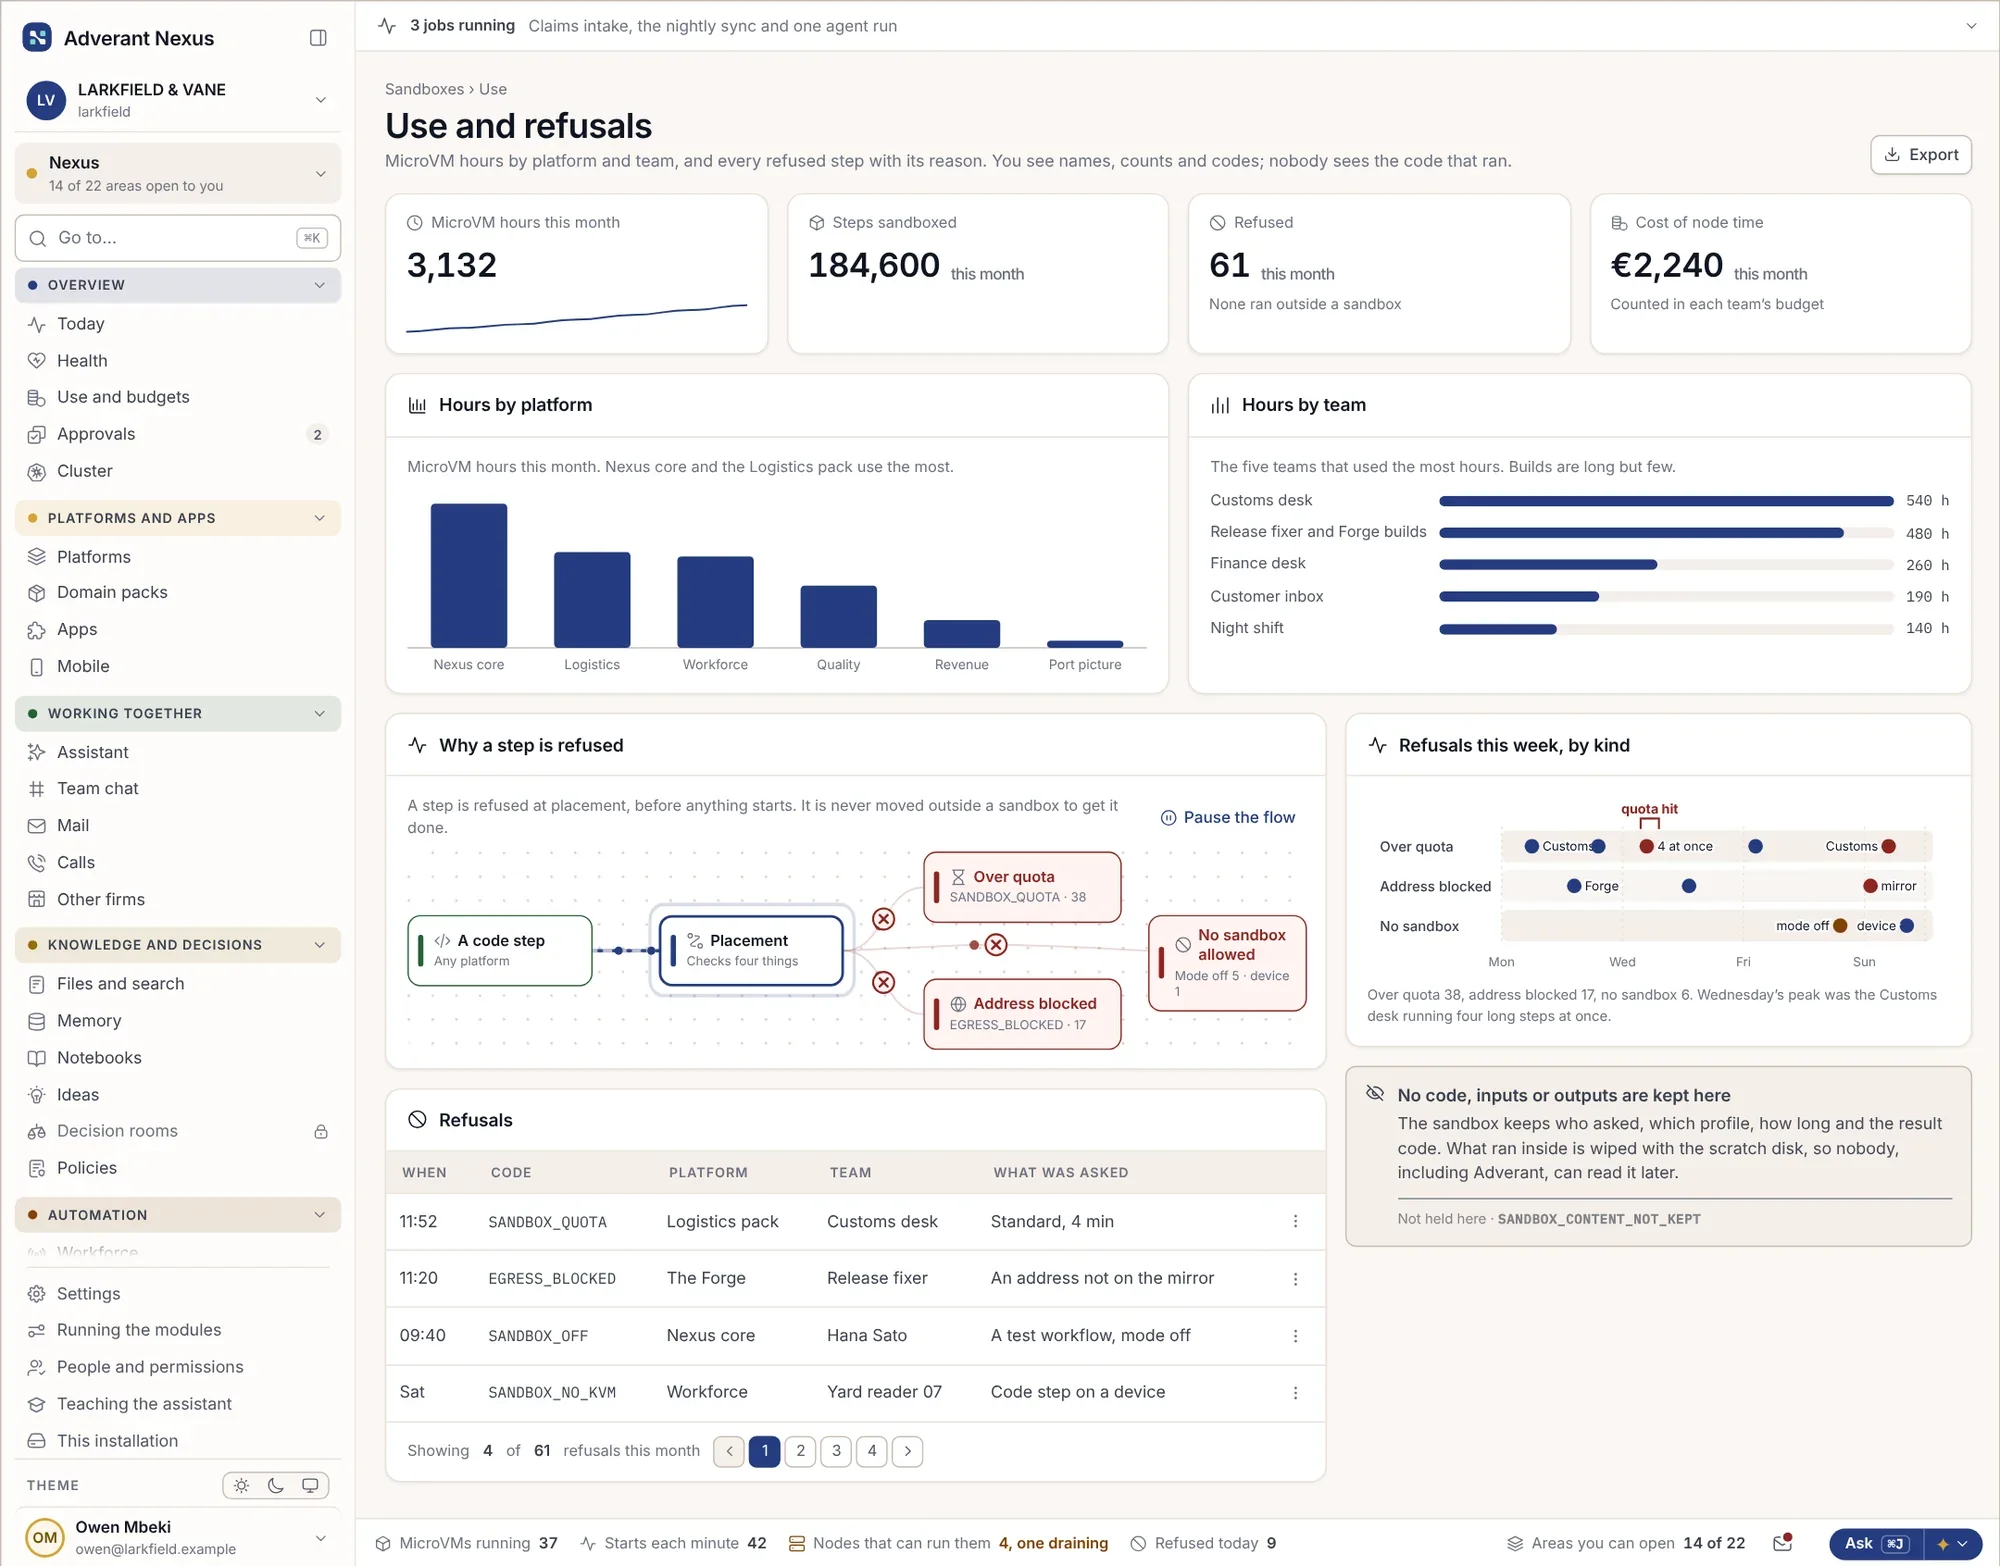
See sandbox use and every refusal, by team and profile. Nobody sees the code that ran.
- Use by team and profile
- Every refusal listed
- Code itself never shown
About sandboxes.
What runs in a sandbox?
Code written by AI agents, files being opened, builds, tests and plugin steps. Anything that could do harm if it misbehaved.
Does it slow things down?
Machines are kept warm, so most steps start in well under a second.
Go deeper
Run something risky, safely.
We will show an AI agent writing and running code inside a sandbox, and what happens when it tries to reach further.